Evergreen Aviation Technologies Corporation detected a cyberattack targeting certain internal information systems on 2026-09-15 and quickly isolated the affected access points. A forensic investigation is underway with external technical support, while core operations continue normally and no sensitive personal data exposure has been identified. #EvergreenAviationTechnologiesCorporation
Category: Cyber Attack
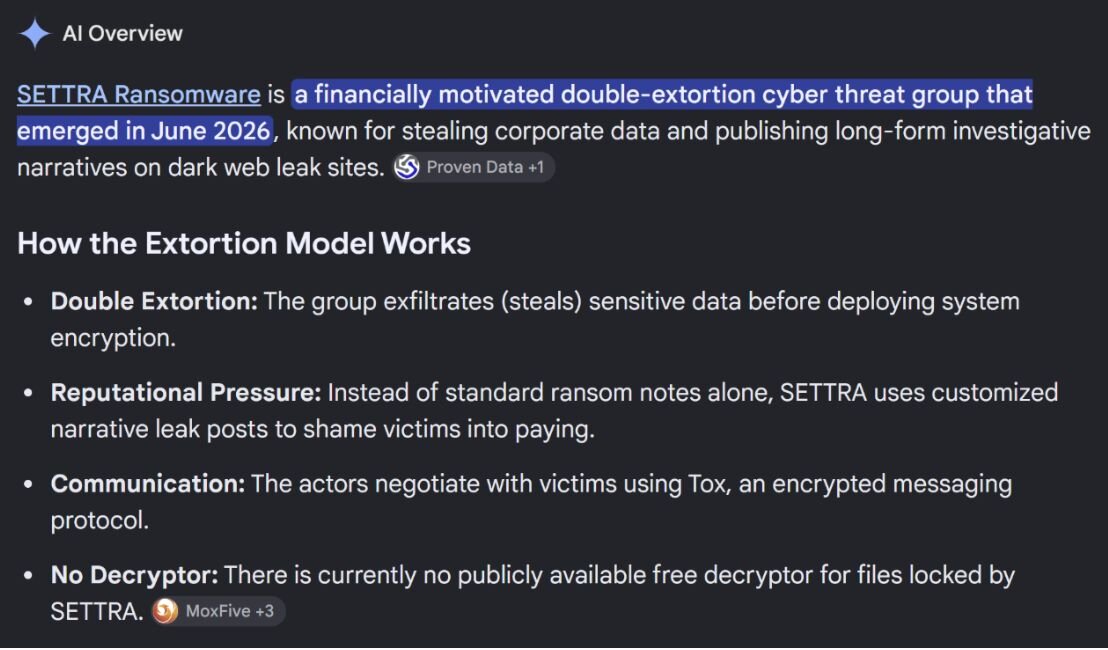
Huntress observed two Settra ransomware incidents, one in July and one in September, affecting organizations in consumer services and retail and in manufacturing. The attackers used MeshAgent RMM, attempted to hide their activity, and in one case showed evidence of BYOVD while also disabling recovery options and clearing Windows Event Logs. #Settra #MeshAgent #gdrvsys #RESTOREFILES
The Court of Appeal for Ontario ruled that Panasonic Canada’s ransomware-related insurance claim is subject to a $3 million USD retention under XL Specialty’s Endorsement #023, not the $1.5 million USD retention under the base policy. Because Panasonic’s loss was valued at about $2 million USD, the court held the claim was wholly self-insured and dismissed Panasonic’s application. #PanasonicCanada #XLSpecialty #Endorsement023
A forum actor named seraphims is advertising an alleged Generation Tux customer dataset with more than 2.8 million records, claiming it was taken in an August 2026 breach via authentication-bypass SQL injection. The unverified listing says the data includes names, emails, phone numbers, password hashes, and address details, and is being…
A forum actor known as ChimeraZ is claiming to sell a JSON database tied to IAD Group – NosRezo, a French professional referral network, with data on 413,722 people. The unverified listing says the archive contains customer and advisor contact details, service information, and fee amounts, and it is being offered…
A forum actor calling themselves mrwho claims to be selling the full bf.st codebase and database, alleging the forum was compromised during its launch period through a vulnerability in the forum implementation. The post shows a 128-table database listing and sample user records, but the claim remains unverified and payment is…
The Maison du souvenir de Maillé was hit by a ransomware attack that encrypted and locked access to more than twenty years of photographs, research documents, and testimonies. The attackers demanded a $5,000 Bitcoin ransom, and the incident also exposed personal data, including members’ email addresses. #MaisonDuSouvenirdeMaillé
A cyberattack crippled the municipal IT support of Collado Villalba City Council, bringing down the municipality’s electronic website and forcing the closure of both citizen service offices. The council later confirmed the incident was a deliberate attack and reported it to the Guardia Civil while coordinating analysis with the Madrid Community’s Digitalization Department. #ColladoVillalba #AyuntamientoDeColladoVillalba #GuardiaCivil #ComunidadDeMadrid
OpenAI’s Project Lily uses outsourced prompt reviewers to manually inspect real ChatGPT conversations in order to improve response quality, while imperfect privacy filters can still expose sensitive user details and memory summaries. The reviewers focus on style and tone rather than factual accuracy, raising concerns that many users may not realize…
An actor using the name Sc0rp10nn is allegedly offering access to Hidalgo C5’s emergency dispatch system in Mexico, claiming persistent backdoor access from an earlier compromise. If true, the access could expose live incidents, caller details, and dispatch operations, while enabling false reports, patrol redirection, and assignment cancellation. #HidalgoC5 #Sc0rp10nn #Carbyne…
A forum actor calling themselves ChimeraZ claimed to have leaked 75 GB of data from Papouille France, totaling 240,177 files. The post reportedly includes email records, CRM contact data, and document metadata, but the claim remains unverified. #PapouilleFrance #ChimeraZ #BlgCloud…
A forum actor known as Venus1337 claims to be selling data from AFTT and FRBTT, including 66,852 subscriber records, 17,441 user records, and credentials for 87 club administrator accounts. The alleged breach involved a file-upload RCE, a deployed web shell, hardcoded database credentials in secret.php, and plaintext admin passwords, but the…

A Swiss court has sentenced a 52-year-old Ukrainian ransomware developer to 12 years and nine months in prison for helping power LockerGoga, MegaCortex, and Nefilim operations. The case is tied to attacks on Stadler Rail, Meier Tobler, and Crealogix, while alleged mastermind Volodymyr Tymoshchuk remains on the FBI’s most wanted list. #LockerGoga #MegaCortex #Nefilim #StadlerRail #VolodymyrTymoshchuk
Anthropic’s AI safety report exposed that the company can access full user logs, including prompts, questions, and uploaded files, raising serious confidentiality concerns for enterprise customers. As a result, organizations such as Nvidia, Palantir, Booz Allen Hamilton, and an unnamed utility company have restricted or rejected Claude use due to Anthropic’s…
Revolut confirmed a data security incident in which attackers impersonated a government body using a legitimate government-domain email address to trick the company into sharing sensitive customer information. The leaked data may include passports, driving licenses, selfies, account statements, IBANs, and transaction histories, creating long-term risks of identity theft, phishing, and…