A forum user known as exfilar claims to be selling a complete live extraction from FLY’s backend after Firebase rules were left absent, making Firestore and Cloud Storage readable and writable without authentication. The alleged dump includes rider resident registration numbers, plaintext passwords, customer delivery details, payment credentials, and other sensitive…
Category: Cyber Attack
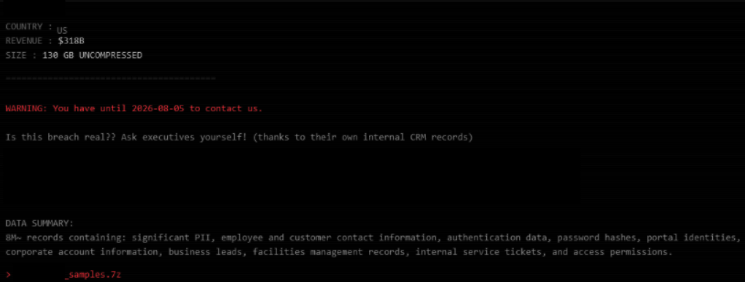
Starknex reported a widespread default-configuration exposure in Microsoft Dataverse and Microsoft Power Pages that could allow unauthenticated or guest users to read sensitive records, including Microsoft Entra ID user data, PII, documents, tickets, and portal credentials. The advisory also linked the issue to active threat actor activity by Exfilsquad, while detailing remediation steps such as Conditional Access, auditing, Web API shutdown, and table-permission reviews. #MicrosoftDataverse #MicrosoftPowerPages #Exfilsquad #BillGate
Brazosport College’s systems remained offline after a cybersecurity incident with an unknown cause. The college discovered the incident on Monday and brought in external specialists to investigate. #BrazosportCollege
A threat actor using the name konata_izumi_shell claims to have breached Bolivia’s Agencia Estatal de Vivienda and exposed 36,046 staff records in SQL format. The alleged dump includes full names, CI identity card numbers, and job roles, and the claim remains unverified. #AgenciaEstataldeVivienda #Bolivia #konata_izumi_shell #CIidentitycardnumbers…

This investigation links Quake3, chromium, and evilcore to one operator who openly identified himself as morgot on exploit.in, while forum logs and private messages show synchronized account activity on the same IPs. The file also ties his long-running malware, loader, and botnet work to the REvil source-code developer persona later associated with Anatoly Sergeevitsch Kravchuk. #Quake3 #morgot #Rcode #REvil #AnatolyKravchuk
A seller using the name palmbeachpete is allegedly offering the EnformionGO database for $50,000, claiming it contains 315.6 million people profiles with emails, phone numbers, and detailed address histories. The listing is unverified, but the sample data suggests a highly sensitive life-record dataset tied to EnformionGO and Enformion. #EnformionGO #Enformion #palmbeachpete…
A forum user named 4me44 allegedly leaked 20,274 records from EVA’s Nantes Sud location in France, exposing personal data such as names, email addresses, dates of birth, phone numbers, and home addresses. The actor also claimed back office admin access and showed a campaign generating €1M in gift cards, but the…
An actor calling themselves sta6 is allegedly selling a breach dataset tied to Zro Global’s hiring platform, claiming access to 55,866 candidate records, interview audio, and internal scoring data. The exposure could reveal sensitive personal and recruitment information, but the claim remains unverified and Zro Global has not publicly addressed it….
ZeroBytes claims a second intrusion against France’s DGFiP cadastral data server, alleging 252,149 extracted rows and exposure of 2,041,778 property holders. The group says it still has access through valid credentials and a multi factor authentication bypass, and is offering that access for sale, though the claim remains unverified. #ZeroBytes #DGFiP…
A forum user calling themselves ChimeraZ allegedly released 16GB of Chupin data, including emails, CRM records, and invoices, in what is labeled the sixth leak tied to tenants of a shared business platform. The numbering and embedded platform identifiers suggest multiple companies may be exposed through the same provider, but the…
CSDD was targeted in a complex and focused cyberattack that led to the exposure of historical payment data containing customers’ personal information. Authorities say the attack has been stopped, the investigation is ongoing, and residents are being warned to watch for possible fraud attempts. #CSDD #CERTLV
Darlington County, South Carolina, isolated parts of its computer systems after a cybersecurity incident disrupted phone lines and some government services, while 911 remained operational. Officials have brought in outside specialists and law enforcement, but the full scope of the attack and whether data was compromised remain unclear. #DarlingtonCounty #SouthCarolina
An actor using the name exfilar claims to have exposed an unsecured Belgian consumer database containing 148,251 records, including bank account numbers, birth dates, names, addresses, and contact details. The alleged leak is unverified, but the combination of IBANs, home addresses, and dates of birth could enable fraud and impersonation. #Belgium…
A seller named exfilar is offering Branch deep link keys for $15,000, advertising access to public developer packages rather than a direct breach. The listing could enable phishing through a shared domain trusted by 2,553 apps, including 666 iOS apps and 1,887 Android apps. #Branch #exfilar…
ZeroBytes claims to have breached the French tax administration through internal VPN credentials and is offering a partial database containing 678,438 taxpayer records. The alleged data includes access to internal search tools for individual and business taxpayers, but the claim remains unverified and has not been publicly addressed by the French…