*Total Post : 18661 Cybersecurity News (auto update every day)
-
Cybersecurity News | Daily Recap [08 Oct 2026]
Please provide the list of cybersecurity news items you want included in the “Daily Recap,” and I’ll convert them into a 2-sentence English summary that starts with “Daily Recap, ” and ends with precise hashtags for the specific malware, threat actors, and affected organizations/systems mentioned. Once you share the news items (or paste the article text), I’ll extract the relevant names/keywords and format the hashtags as #Keyword1 #Keyword2 without using broad tags like #malware, #ransomware, or #cybersecurity.
-
Anthropic Launches Free AI Vulnerability Scanner for Open-Source Projects
Anthropic has launched OSS Scanner, an opt-in AI vulnerability scanning service for open-source projects that uses its strongest models to generate automated security reports without human review. The initiative is part of Anthropic’s broader effort to strengthen critical infrastructure and open-source software while helping defenders find and fix flaws faster. #Anthropic…
-
Researchers Publish Working Exploit for Pre-Auth AnyDesk Linux Flaw That Gives Root Access
Researchers published the AnyPwn exploit for a pre-authentication remote code execution flaw in AnyDesk Linux that can lead to root access before a connection is approved. AnyDesk fixed the issue in version 8.0.3, but the bug was initially disclosed without a CVE or formal security advisory, and the exploit targets AnyDesk…
-
TP-Link Sued by Four More U.S. States Over Router Security and China Ties
Four U.S. states sued TP-Link Systems, accusing it of misleading consumers about router security and its separation from China, while TP-Link denied the claims and said it will fight them in court. The complaints also cite exploited flaws in TP-Link devices, state-backed hacking activity, and a new FCC approval push for…
-
FBI disrupts Flax Typhoon hacking tools used in global cyberattacks
The FBI seized seven domains used by Microscan and FishHub, two hacking tools tied to Chinese state-sponsored hackers known as Flax Typhoon and linked to Integrity Technology Group. The tools were used to scan and compromise organizations worldwide, including U.S. critical infrastructure, Taiwanese universities, and airports in Japan and Poland. #FlaxTyphoon #IntegrityTechnologyGroup #Microscan #FishHub
-
Anthropic offers free AI security scans to open-source maintainers
Anthropic’s OSS Scanner is a free AI-powered service that scans open-source projects for security vulnerabilities and sends maintainers detailed reports with reproduction steps and, when possible, fixes. The service builds on Project Glasswing and aims to speed up disclosure while leaving project teams responsible for validating and prioritizing findings. #Anthropic #OSSScanner #ProjectGlasswing #Claude #OpenSSL
-
High-severity NVIDIA vulnerability lets unauthenticated attackers crash GPU monitoring
Hundreds of internet-exposed GPU servers were found running vulnerable NVIDIA DCGM Exporter instances affected by CVE-2026-47483, which can be crashed by unauthenticated attackers and may disrupt AI workloads. The exposed monitoring services also leaked detailed GPU, server, and network information across thousands of systems, with impacts seen in environments tied to NVIDIA, Voltage Park, and other providers. #NVIDIA #DCGMExporter #CVE2026-47483 #VoltagePark
-
Unpatched AhsayCBS Vulnerabilities Exploited in the Wild
Hackers are actively exploiting two unpatched AhsayCBS vulnerabilities, CVE-2026-105133 and CVE-2026-105134, to achieve unauthenticated remote code execution, deploy webshells, and gain persistence on exposed systems. Huntress says at least five organizations have been targeted, with attackers also installing XMRig miners, abusing a vulnerable driver, and disguising malicious components as Microsoft Edge….
-
Google Domains Impacted by Recent ccTLD Hijacks
Google said several of its domains were affected by a hijack of third-party ccTLDs, including .gh, .sl, and .as, which allowed attackers to alter DNS records and obtain unauthorized HTTPS certificates. The company blocked the certificates in Chrome, worked with CAs to revoke them, and urged domain owners to monitor Certificate…
-
In Other News: AI Used in Korean Bank Breaches, Poem-Guided Botnet, Empire Admin Gets 40 Years
This week’s roundup covers malware, supply chain abuse, exposed infrastructure, and high-profile criminal cases, including PoeLLM, GhostAction, and a compromised Tensorlake npm SDK. It also highlights notable developments involving CISA, Nvidia DCGM Exporter, South Korean bank attacks, and the sentencing of the Empire Market co-founder. #PoeLLM #GhostAction #Tensorlake #CISA #Nvidia #DCGMExporter…
-
What the BPFDoor backdoor tells us about attacks on the network edge
BPFDoor is a stealthy Linux backdoor that waits for a “magic packet,” making it unusually hard to detect and especially dangerous in telecom and edge-device environments. Christiaan Beek of Rapid7 Intelligence explains why attackers target mail gateways, VPNs, and other appliances, and how CISOs should report visibility gaps honestly to the board. #BPFDoor #Rapid7Intelligence #Linux
-
October 2026 Patch Tuesday forecast: Time for an Office cleanup
September 2026 Patch Tuesday set a Microsoft record with 973 CVEs addressed, while only two vulnerabilities were known exploited and none were publicly disclosed. The update roundup also highlighted Office end-of-support migration issues, Apple’s macOS 27 Golden Gate release with a zero-day fix, and Windows 11 26H2 arriving alongside other important Microsoft fixes and upcoming support cutoffs. #CVE-2026-85880 #CVE-2026-81963 #KB5002907 #CVE-2026-86950 #Windows11 26H2 #Office2016 #Office2019 #macOS27 #GoldenGate
-
Product showcase: SimpleLogin keeps your email address private with aliases
SimpleLogin, a Proton email alias service, lets users create separate forwarding addresses to protect their primary inbox, reduce tracking across websites, and manage unwanted messages more easily. In testing, alias creation, forwarding, and replies worked smoothly, with support for browser extensions, mobile apps, and strong account security options. #SimpleLogin #Proton
-
Google Pixel 10 Exploits Earned Hackers $560,000 at Pwn2Own
Pwn2Own Ireland 2026 ended with researchers earning more than $1.2 million for exploits against phones, printers, smart speakers, smart home hubs, AI infrastructure, coding tools, and cloud databases. Google Pixel 10 hacks brought in the biggest payouts, while Sonos, Oracle, OpenAI Codex, Nvidia Dynamo, LiteLLM, Philips Hue Bridge Pro, Samsung Galaxy…
-
Citrix Urges Immediate Patching of Critical NetScaler Vulnerability
Citrix has warned that a critical NetScaler flaw, tracked as CVE-2026-107406, could enable remote code execution or denial-of-service and needs immediate patching. The issue affects certain NetScaler ADC, NetScaler Gateway, and Secure Private Access Hybrid deployments, and Citrix says no unmitigated exploits are known at this time. #Citrix #NetScaler #CVE-2026-107406…
-
Anthropic Fast-Tracks AI Bug Reports to OSS Maintainers, Taps 11 Firms for OT Security
Anthropic announced OSS Scanner, a free opt-in service that sends AI-generated vulnerability reports directly to open source maintainers without human review, along with suggested fixes and PoCs. It also launched the Critical Infrastructure Defense Program to help OT providers and their partners identify and remediate long-standing security flaws in essential systems…
-
Companies want autonomous IT operations but hesitate to let AI act alone
Ninety percent of companies want to move toward autonomous IT operations in the next two years, but most still want a human to approve AI decisions and lack the visibility, automation, and governance needed to support that shift. The report also says AI is already changing service desk work, with many teams using it to detect and fix issues before employees notice. #agenticAI #AIcodeSprawl
-
Formula Predicts When AI Chatbots Are at Risk of Turning Bad
Researchers from George Washington University say they can model when an AI system may tip into producing undesirable outputs by analyzing its attention dynamics and prompt history. Their findings suggest early-warning controls could help reduce rogue behavior in open-weight transformer models, though it cannot be fully eliminated. #GeorgeWashingtonUniversity #NeilJohnson #FrankYingjieHuo…
-
Anthropic rolls out program for ‘long-term commitment’ to secure critical infrastructure, open source software
Anthropic has launched a new critical infrastructure defense program that pairs Claude models and its security expertise with major cybersecurity companies to find and fix vulnerabilities in critical infrastructure and open-source software. The initiative includes a new opt-in scanning service for open source projects, aiming to speed up reporting, suggest patches, and strengthen defenses before weaknesses can be exploited. #Anthropic #Claude #Accenture #BoozAllen #CrowdStrike #Deloitte #Dragos #Hitachi #InsaneCyber #NozomiNetworks #PaloAltoNetworks #PwC #RockwellAutomation
-
Leader of 764 pleads guilty, faces up to 30 years in prison
Prasan Nepal, also known as “Trippy,” pleaded guilty to conspiracy to commit sexual exploitation of a child for his role in helping lead the 764 child sextortion network. Prosecutors say he and his co-conspirators used 764 and its 764 Inferno subgroup to groom, extort, and abuse minors across multiple jurisdictions. #764 #764Inferno #PrasanNepal #LeonidasVaragiannis #TheCom
Cybersecurity News Sources
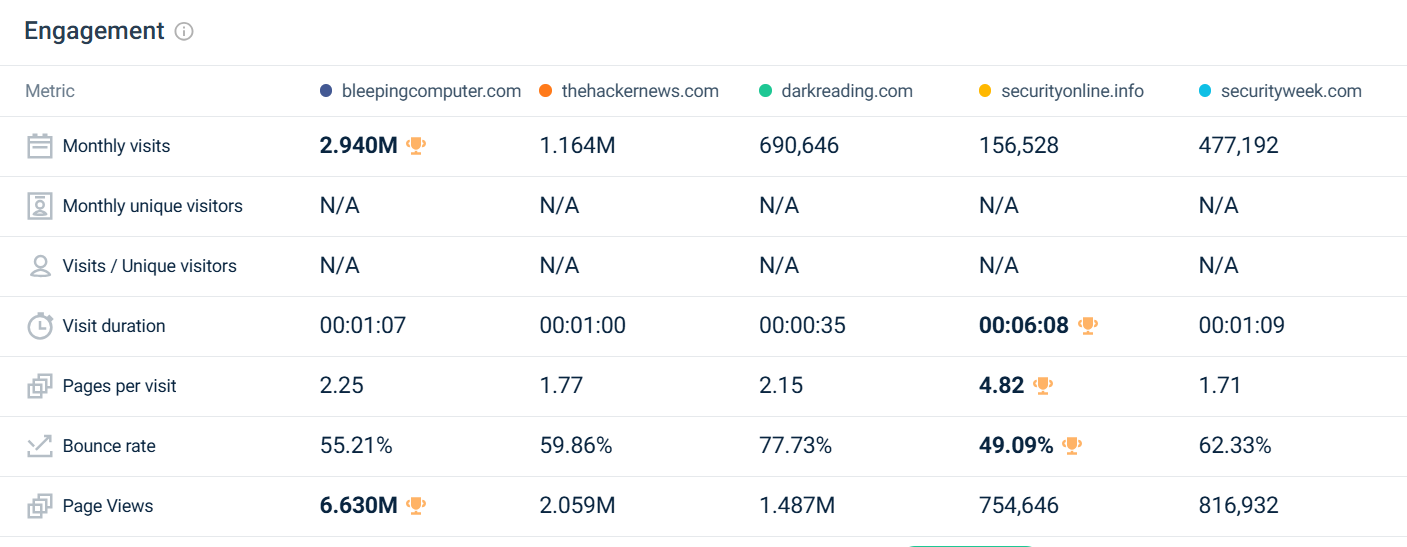
This site will aggregate Cybersecurity News from this sources:
- securityonline.info
- bleepingcomputer.com
- thehackernews.com
- darkreading.com
- + News from Cyware (Currated by Cyware)
- + Latest 100 cyberattacks referenced by Valéry Marchive
- + News from Immuniweb (Cybercrime Investigation and Prosecution)
- + Other hundreds of News Portal
Reference for Security News
Sorted by estimated “Number of Articles” per week. a/w = articles / week.
- malware.news (260 a/w)
- securityboulevard.com (140 a/w)
- ScMagazine.com (70 a/w)
- DarkReading.com (58 a/w)
- BankInfoSecurity.com (48 a/w)
- bleepingcomputer.com (47 a/w)
- CySecurity.news (40 a/w)
- SecurityWeek.com (40 a/w)
- BleepingComputer.com (40 a/w)
- Thecyberexpress.com (34 a/w)
- TheHackerNews.com.com (32 a/w)
- HelpNetSecurity.com (32 a/w)
- PacketStormSecurity.org (30 a/w)
- SecurityAffairs.com (29 a/w)
- Therecord.media (29 a/w)
- TheRegister.com (28 a/w)
- Infosecurity-Magazine.com (26 a/w)
- Securityonline.info (69 a/w)
- Csoonline.com/asean/security/ (19 a/w)
- Hackread.com (19 a/w)
- MalwareBytes.org (14 a/w)
- Cybersecuritydive.com (12 a/w)
- CyberScoop.com (11 a/w)
- Techrepublic.com/topic/security/ (11 a/w)
- ITSecurityGuru.org (9 a/w)
- Zdnet.com/topic/security/ (8 a/w)
- TripWire.com (6 a/w)
- Arstechnica.com/security/ (5 a/w)
- Latesthackingnews.com (5 a/w)
- Asec.ahnlab.com (4 a/w)
- Blog.polyswarm.io (3 a/w)
- Kroll.com/en/ (3 a/w)
- Mandiant.com (2 a/w)
- Bitdefender.com/blog/labs/ (1 a/w)
Check this also :
Update November 2024
“I have launched several social media platforms for updates on Security News”