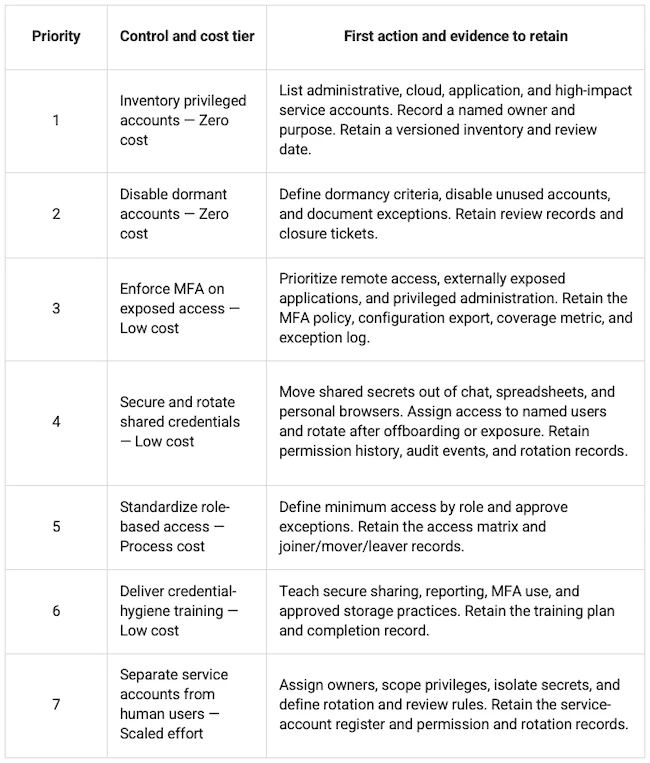
NIS2 credential security starts with low-cost, risk-based controls that make access visible, revocable, and reviewable, helping teams build audit-ready evidence without waiting for a full programme. The article prioritizes privileged and shared credentials, MFA for high-risk access, and structured vaulting and logging through Passwork to support Article 21 requirements. #NIS2 #Article21 #VerizonDBIR #Passwork
Keypoints
- NIS2 credential controls should be chosen based on actual organizational risk.
- Privileged, shared, and service credentials are the highest-priority targets.
- MFA should be deployed first on exposed, remote, and administrative access.
- Audit-ready evidence needs logs, review dates, and exception records.
- Passwork supports inventory, access control, and credential rotation for NIS2 evidence.
Read More: https://www.helpnetsecurity.com/2026/10/06/passwork-nis2-credential-security/