Google Threat Intelligence Group found that vulnerability disclosures doubled in 2026 while real-world exploitation remained rare, yet attackers moved quickly to weaponize newly disclosed flaws. The report highlights rapid abuse of an AI-discovered issue in BeyondTrust Privileged Remote Access and Remote Support, along with growing targeting of AI software such as Flowise, Langflow, vLLM, Ollama, and LiteLLM. #CVE-2026-1731 #BeyondTrust #SNOWLIGHT #SPARKRAT #LiteLLM #Langflow #Flowise #vLLM #Ollama
Keypoints
- Vulnerability disclosures doubled in 2026, but only a small fraction were exploited in the wild.
- Zero-day exploitation increased, while most exploitation growth came from n-day vulnerabilities.
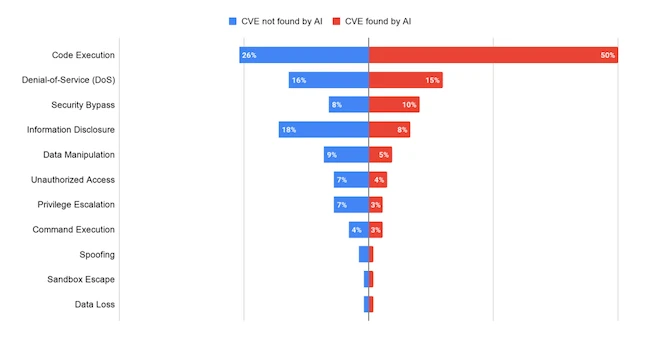
- AI-discovered vulnerabilities were more likely to lead to remote code execution.
- Attackers exploited CVE-2026-1731 within days of disclosure and used it to deploy payloads and steal data.
- AI orchestration and serving tools such as Flowise, Langflow, vLLM, Ollama, and LiteLLM are major targets.