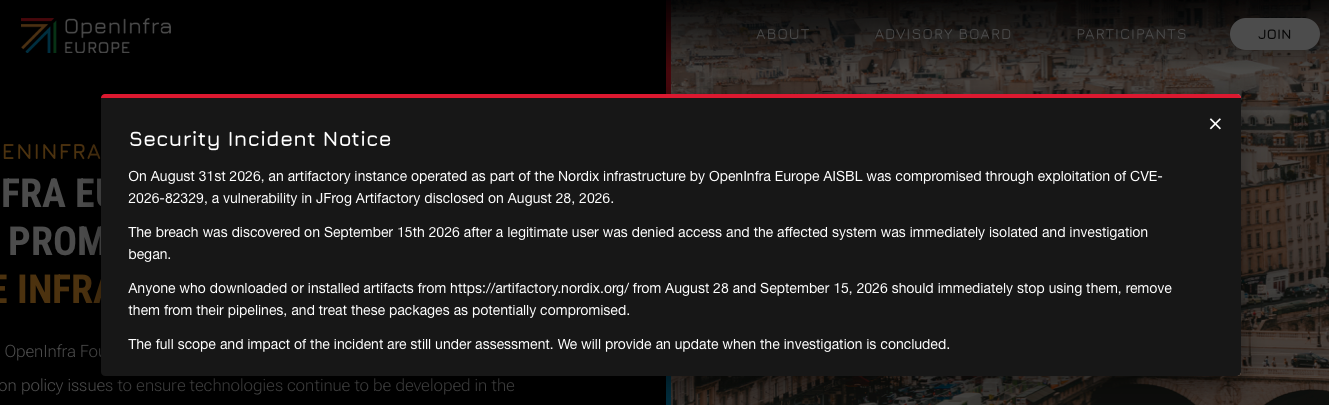
Attackers compromised a self-hosted JFrog Artifactory instance operated by OpenInfra Europe by exploiting CVE-2026-82329, an authentication bypass flaw that granted admin-level access. OpenInfra Europe warned anyone who downloaded artifacts from artifactory.nordix.org between August 28 and September 15, 2026 to stop using them immediately and treat them as potentially compromised. #OpenInfraEurope #JFrogArtifactory #CVE-2026-82329
Keypoints
- OpenInfra Europe disclosed a compromise of its self-hosted JFrog Artifactory instance.
- Attackers exploited CVE-2026-82329 to bypass authentication and gain admin privileges.
- Artifacts from artifactory.nordix.org between August 28 and September 15, 2026 may be compromised.
- The incident was discovered after a legitimate user was denied access on September 15.
- The affected system was isolated, and the full impact of the breach is still under investigation.
Read More: https://www.helpnetsecurity.com/2026/09/30/openinfra-jfrog-artifactory-instance-compromised/