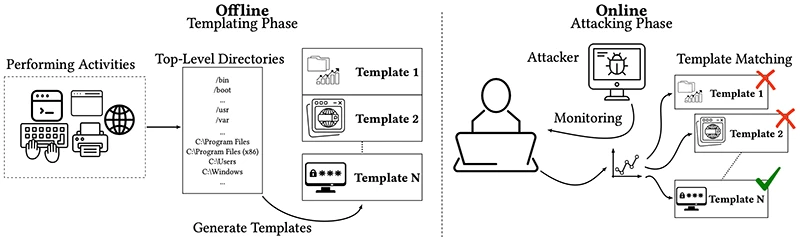
Researchers at Graz University of Technology showed that file-notification systems in Windows, Linux, macOS, and Android can leak sensitive user activity across accounts, including browsing history, keystroke timing, and device events. The paper also describes partial mitigations and reports that the attacks still work on default or lightly protected systems in several cases. #GrazUniversityofTechnology #Windows #Linux #macOS #Android #CVE-2025-68788 #CVE-2025-27738 #CVE-2025-21197
Keypoints
- Windows file notifications can reveal full paths and browsing activity from other users’ profiles.
- Firefox and Edge left detectable site-specific folder traces that exposed visited websites.
- Linux inotify could leak keyboard timing from local input and SSH sessions.
- macOS leaked less, but still exposed app launches, printing, and Bluetooth changes.
- Android FileObserver allowed a zero-permission app to see downloads, photos, screenshots, and WhatsApp media.
Read More: https://www.helpnetsecurity.com/2026/09/28/cve-2025-68788-file-notification-attacks/