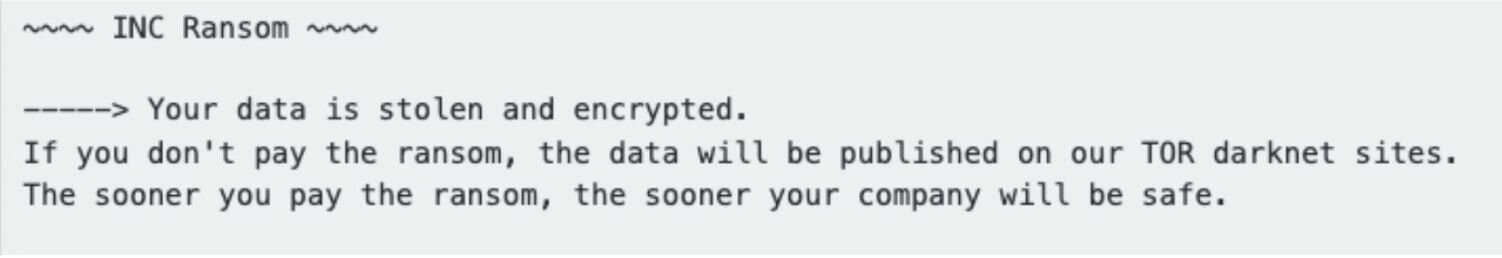
Huntress investigated an August post-incident case involving INC ransomware that impacted at least 175 endpoints, with traces found on domain controllers and evidence of early persistence, lateral movement, and later ransomware deployment. Researchers also uncovered two ransom notes, an AnyDesk-based deployment path, and a BYOVD technique used to load a driver and disable security tools. #INC #AnyDesk #Impacket #HwAudio #HWAuidoOs2Ec.sys
Keypoints
- Huntress responded after INC ransomware had already spread across at least 175 endpoints.
- Investigators found early scheduled tasks, obfuscated PowerShell, and RDP-based lateral movement.
- A second wave used AnyDesk to deploy netscan.exe, a vulnerable driver, and other tools.
- Attackers used BYOVD to load an EDR/AV killer driver and weaken defenses.
- Two ransom notes, INC-README.txt and DATALEAK_PRESS_RELEASE.txt, increased pressure with data-leak threats.
Read More: https://www.huntress.com/blog/two-inc-ransom-notes