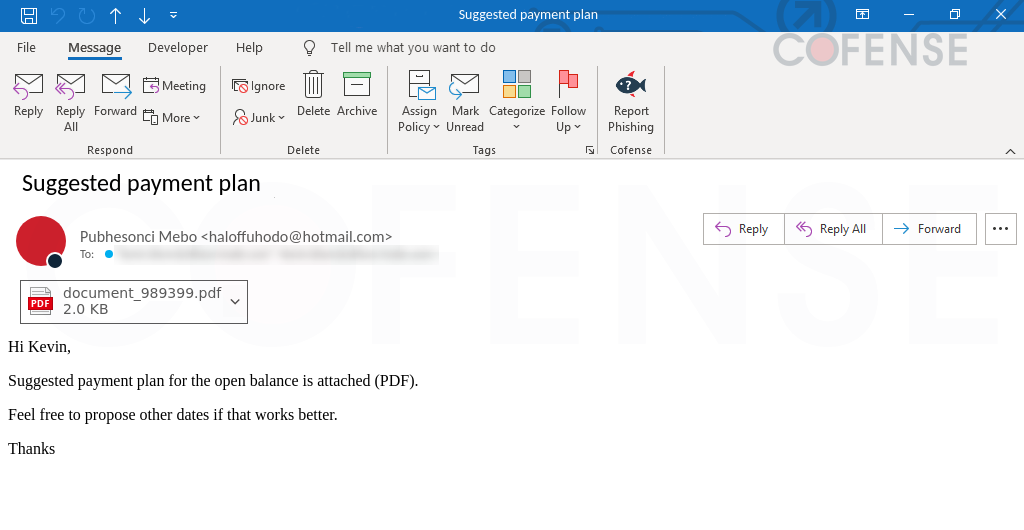
Global Group is a newly observed Ransomware-as-a-Service operation that builds on Black Lock and Mamona to target enterprises with double extortion, data theft, and encryption. It spreads through phishing emails, malicious PDFs, ISO files, and loader activity that ultimately deploys an encryptor and ransom note to pressure victims into paying. #GlobalGroup #BlackLock #Mamona #Cofense #WinMerge
Keypoints
- Global Group operates a Ransomware-as-a-Service model for large-scale enterprise attacks.
- The campaign uses phishing emails with PDF lures to deliver the malware.
- Malicious ISO and EXE files trigger WinMerge.exe to fetch the encryptor payload.
- The ransomware steals data, encrypts files, and threatens public leaks for extortion.
- Victims receive a ransom note with instructions and demands after encryption.
Read More: https://cofense.com/blog/from-payment-plan-to-ransomware-inside-a-global-group-attack