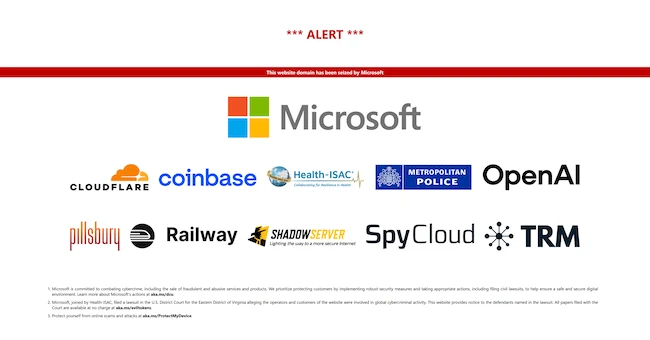
Microsoft-led disruption efforts have taken down the EvilTokens phishing service, which compromised more than 12,000 inboxes across over 10,000 organizations by combining account theft with AI-assisted mailbox analysis. The operation used stolen access to identify financial conversations, impersonate trusted contacts, and prepare fraud at scale, while authorities also arrested two suspects in connection with the service. #EvilTokens #Microsoft #OpenAI #Cloudflare #Coinbase #HealthISAC
Keypoints
- EvilTokens compromised more than 12,000 inboxes across over 10,000 organizations.
- Microsoft and partners seized 50 websites and disabled over 150 related domains.
- The service used an AI chatbot to analyze mailbox contents and assist fraud planning.
- Victims were tricked into entering authentication codes on Microsoft’s legitimate sign-in page.
- Two men were arrested in London in connection with the alleged operation.
Read More: https://www.helpnetsecurity.com/2026/09/23/microsoft-eviltokens-phishing-service-disrupted/