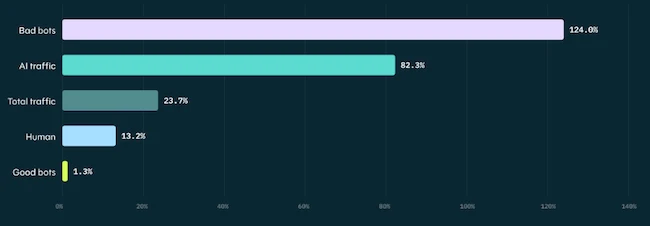
Malicious bot activity surged 124% from July 2025 to June 2026, far outpacing human traffic growth, while AI agent and LLM crawler traffic also rose sharply as attackers expanded scraping, credential stuffing, spam, and DDoS activity. DataDome’s report found that many websites still fail to detect simulated bots, and that AI assistants and malicious automation are increasingly targeting login pages, shopping carts, payment pages, and online forms. #DataDome #LLM #AIagents #CredentialStuffing #WebScraping
Keypoints
- Malicious bot traffic increased 124% in 12 months, far exceeding human traffic growth.
- AI agent and LLM crawler traffic rose 82.3% during the same period.
- Web scraping was the dominant attack type, accounting for 70.9% of bad bot traffic.
- Credential-stuffing attacks showed recurring waves of high-volume activity and pauses.
- Most popular websites failed to detect the simulated bots tested by DataDome.
Read More: https://www.helpnetsecurity.com/2026/09/23/datadome-growing-bad-bot-traffic-report/