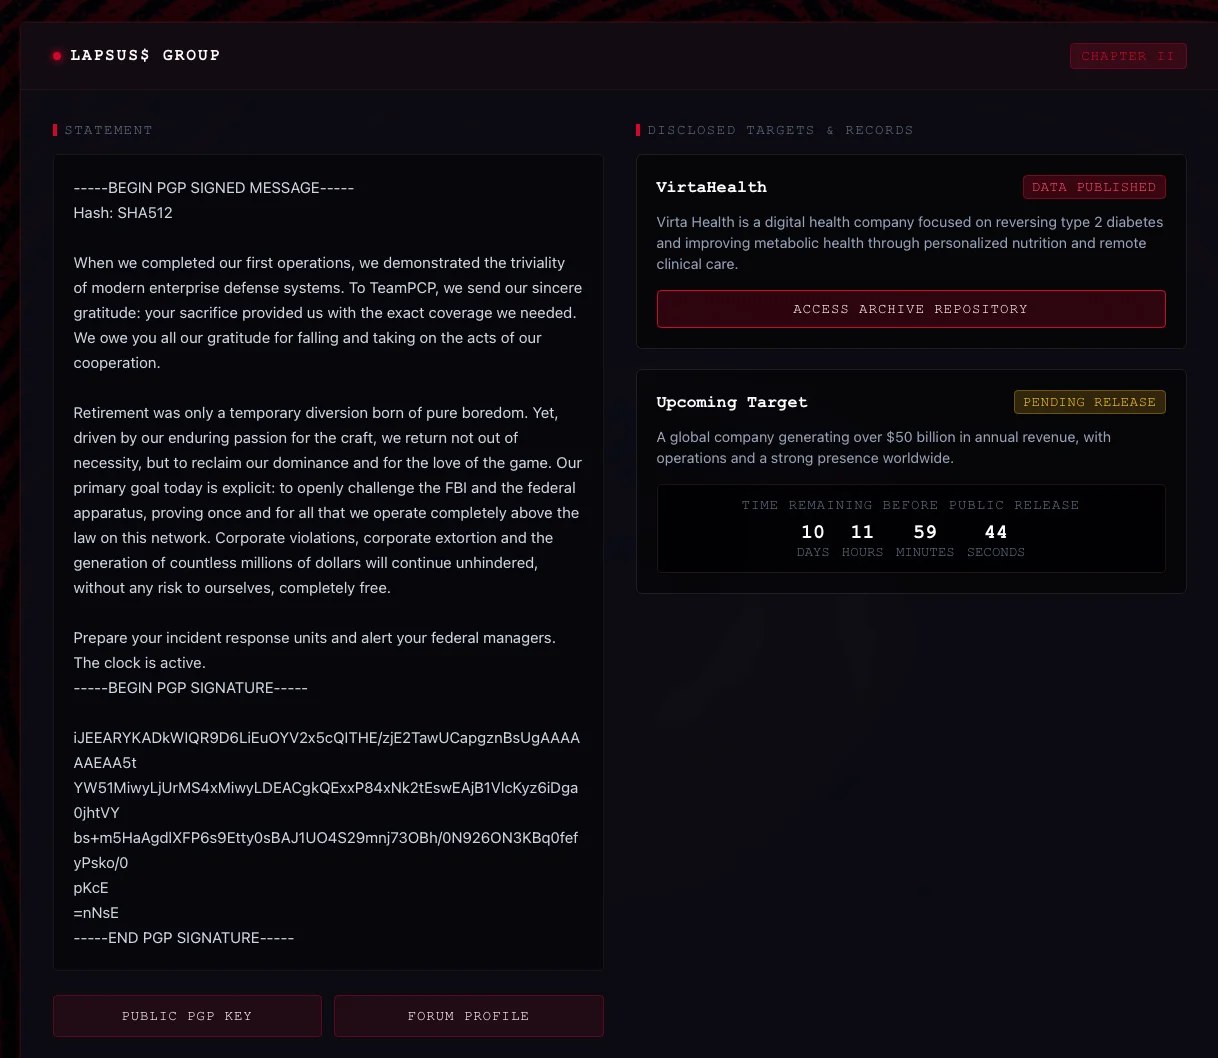
Elsevier’s main website and two portals were briefly redirected to a page branded “LAPSUS$ GROUP, Chapter II,” which included a taunting statement and a countdown to another alleged victim. Researchers say the incident likely involved a DNS or CDN edge change, but Elsevier has not yet explained how it happened or confirmed whether user data was exposed. #Elsevier #LAPSUS$
Keypoints
- Three Elsevier domains were hijacked and redirected to a LAPSUS$-branded page.
- The redirect lasted about 78 minutes before the domains were restored.
- Affected portals included Elsevier.com, Evolve.elsevier.com, and Submit.elsevier.com.
- Researchers suspect a DNS or CDN edge change caused the redirect.
- LAPSUS$ appears to be reviving its brand, though continuity with the original group is unconfirmed.
Read More: https://www.helpnetsecurity.com/2026/09/22/elsevier-domains-hijack-lapsus/