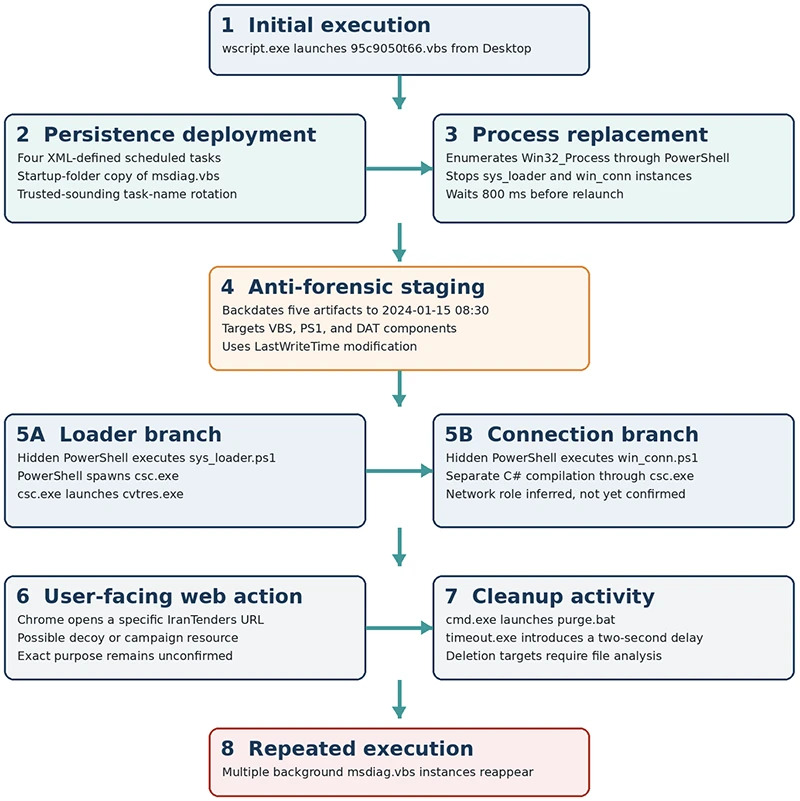
Researchers analyzed TASK#STOMP, a Windows backdoor that hunts for business documents, exfiltrates them, and persists to steal new or modified files while also collecting Wi-Fi credentials, clipboard text, screenshots, and operator commands. Securonix says the malware uses multiple footholds, likely arrives via phishing with a ZIP or ISO/IMG attachment, and shows no clear attribution to a known APT. #TASKSTOMP #Securonix #WindowsScriptHost #VBScript #PowerShell
Keypoints
- TASK#STOMP searches for business documents and uploads them to attacker servers.
- The malware steals saved Wi-Fi passwords, clipboard text, and screenshots.
- It creates multiple persistence mechanisms, including scheduled tasks and a Startup folder copy.
- Securonix found no clear attribution to a known threat actor or APT.
- Defenders should hunt for the hardcoded token, malicious domains, hashes, and the malware’s scheduled tasks.
Read More: https://www.helpnetsecurity.com/2026/09/21/taskstomp-windows-backdoor/