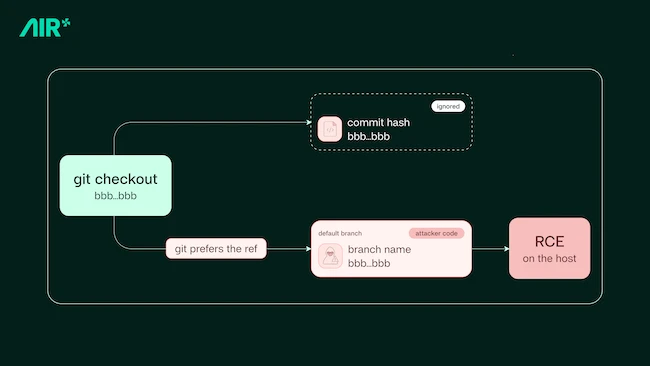
AIR uncovered Plugin4Shell, a zero-click RCE affecting Claude Code, Codex, GitHub Copilot, and Gemini CLI through a shared plugin SHA-pinning bypass. The flaw lets attackers swap in malicious code during background updates, with vendor responses ranging from patches to deprecation and no fix yet for GitHub Copilot. #Plugin4Shell #ClaudeCode #Codex #GitHubCopilot #GeminiCLI #AIR #Anthropic #OpenAI #Microsoft #Google #Antigravity
Keypoints
- Plugin4Shell is a zero-click RCE affecting four major AI coding agents.
- The bug breaks SHA pinning and enables plugin code swapping without user action.
- Background auto-updates can reintroduce the malicious code after installation.
- Attackers can abuse a trusted plugin or hijack an existing repository.
- Anthropic and OpenAI patched their agents, while Microsoft has not and Google deprecated Gemini CLI.
Read More: https://www.helpnetsecurity.com/2026/09/18/plugin4shell-ai-coding-agents-vulnerability/