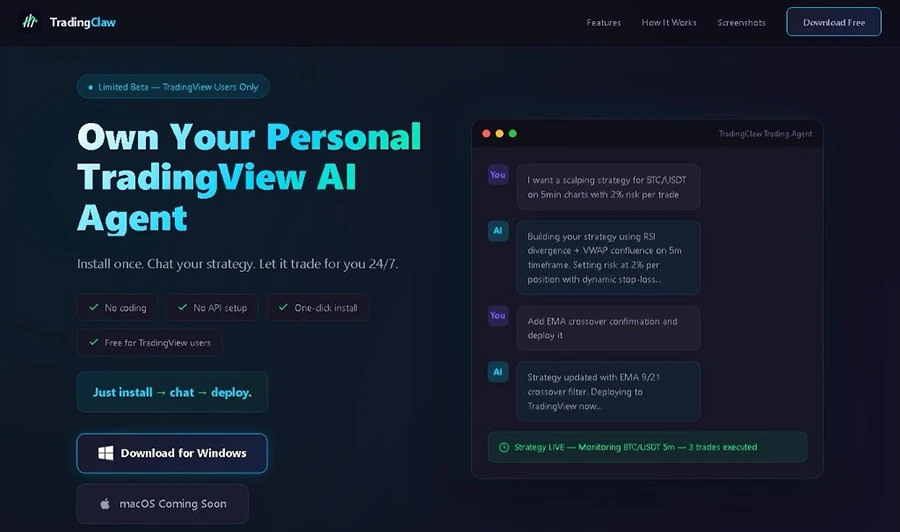
HP identified a fake AI crypto trading agent website that delivered Needle Stealer, which swaps browser wallet extensions to steal passwords and give attackers control of funds. The company also tracked QR code phishing, Phantom Stealer, and other fake installer campaigns that used image-based payloads, DLL side-loading, and process injection to spread theft tools. #NeedleStealer #PhantomStealer #MetaMask #CoinbaseWallet #Phantom #TradingClaw #CloudflareTurnstile #OneDrive #XWorm #PureLogsStealer #Formbook
Keypoints
- Needle Stealer was delivered through a fake AI crypto trading agent website.
- The malware replaced browser wallet extensions and stole wallet passwords.
- The campaign targeted users of MetaMask, Coinbase Wallet, Phantom, and other wallet extensions.
- HP also observed QR code phishing that pushed victims from desktop to mobile devices.
- Phantom Stealer and other loaders were spread through image-based payloads, HTML smuggling, and fake installers.
Read More: https://www.helpnetsecurity.com/2026/09/17/fake-ai-trading-agent-research/