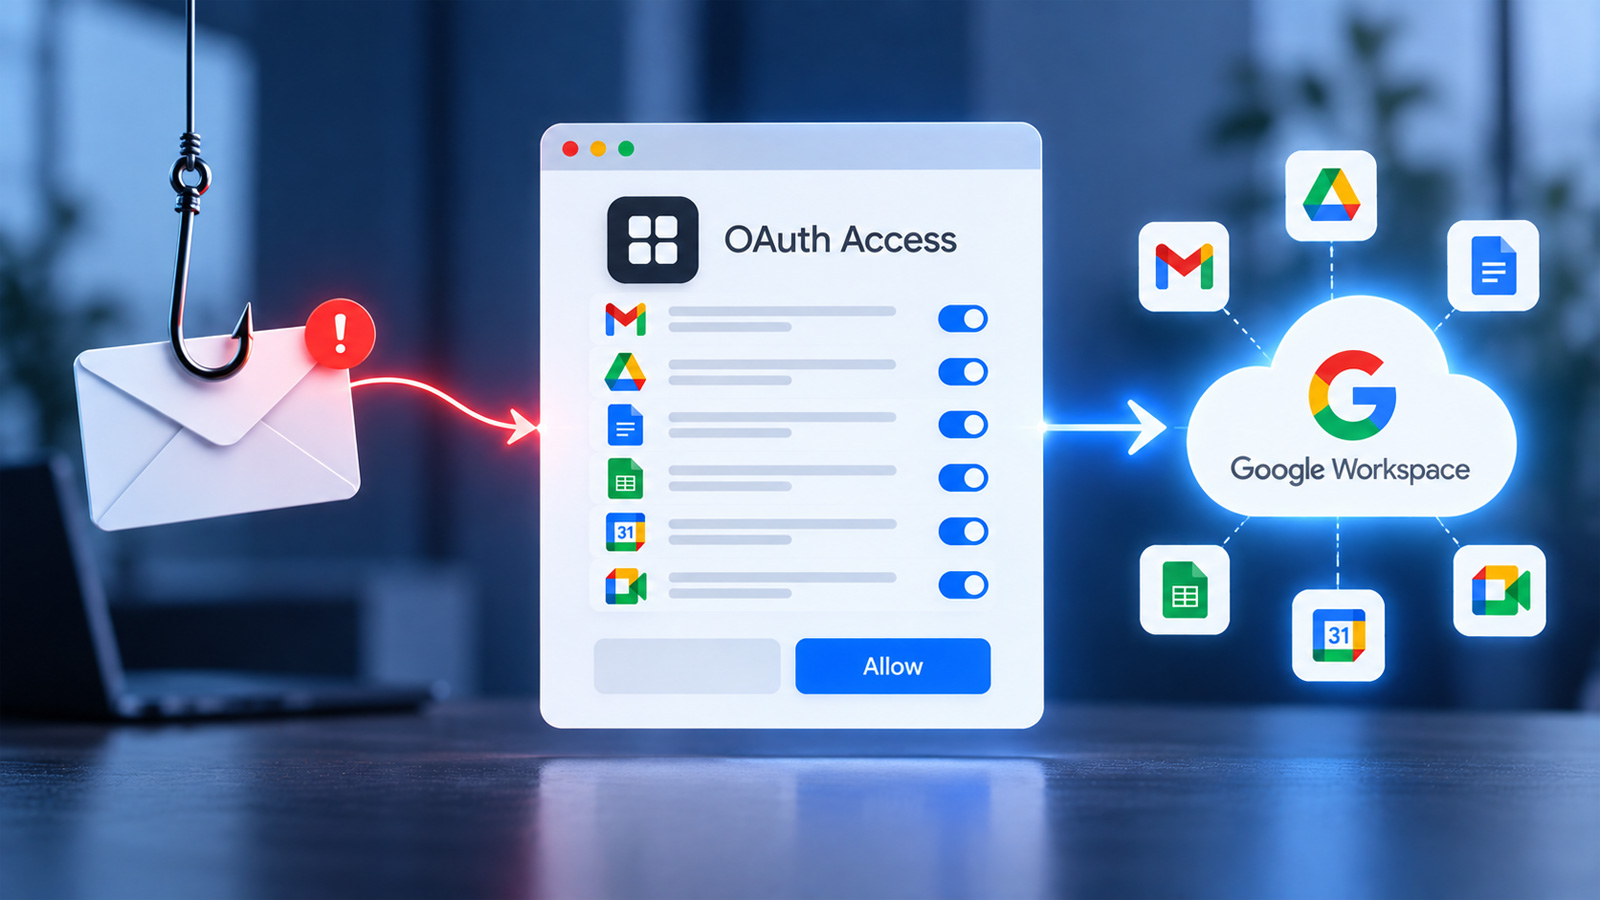
Google Workspace attackers can gain access without stealing passwords by using malicious OAuth applications and social engineering to trick users into authorizing access. A BleepingComputer webinar with Material Security will examine two real attacks, the early response decisions that mattered most, and the controls organizations should prioritize to better protect Google Workspace. #GoogleWorkspace #OAuth #MaterialSecurity #BleepingComputer
Keypoints
- Attackers can breach Google Workspace without exploiting a software flaw or stealing a password.
- Malicious OAuth apps can abuse user-granted permissions to access sensitive data.
- Social engineering is used to convince victims to authorize harmful applications.
- The webinar will analyze two attacks and the critical first hours of each breach.
- Organizations need visibility into third-party apps and the permissions users can approve.